Category: Hardware Security

  • Is Mobile Banking Safe? Bar Harbor Financial Institution & Belief

    As a result, the popularity of monetary establishments can be compromised. Indeed, the low literacy rate in Sub-Saharan Africa 9 poses a big challenge in terms of whether these cellular banking apps are used. For example, the dearth of literacy can lead users to be victims of fraud or phishing attacks when utilizing apps. Since MBAs process delicate knowledge, they are not without dangers and vulnerabilities. For instance, sensitive keys persist within cell monetary purposes from Africa 4. Such security points may end up in vital monetary losses for each users and monetary establishments.

    API keys, OAuth client secrets and techniques, signing keys, or backend service tokens get embedded directly in the APK or IPA. An attacker downloads the app from the store, decompiles it, and extracts the credentials. Banking apps register many intent handlers for branch lookups, fee confirmations, biometric prompts, and 3DS challenges. The OWASP Cellular Application Security Verification Commonplace (OWASP MASVS) groups the related controls underneath MASVS-AUTH (authentication and session management), MASVS-STORAGE (credential protection), and MASVS-PLATFORM (secure inter-component communication). Designed for high-assurance environments, Signer integrates seamlessly with national eID schemes and belief service providers, to deliver safe, compliant signing operations at scale.

    Stop Bot Attacks

    quantum computing cryptography

    Proper certificate chain checking involves verifying that the server’s certificate is issued by a trusted CA, checking for certificates revocation standing, and verifying the whole certificate chain as much as a trusted root CA. However, if the app fails to verify the certificates chain properly, it could doubtlessly trust a certificate that has not been issued by a trusted certificates authority (CA) or that has been tampered with. As explained above, this might compromise the user’s safety through a man-in-the-middle assault. Bassolé et al. 32 examine Android banking and payment apps in African countries by figuring out specific vulnerabilities and elevating awareness of the safety in these apps. The authors provide valuable info to builders and stakeholders, enabling them to enhance safety measures and defend person information.

    Fixing Important Banking Safety Challenges

    Incorporating a various range of viewpoints out of your engineering and safety groups to collaborate on a risk modeling strategy will have long-lasting optimistic impacts. As Soon As the best dangers to your utility and your users are identified, all of your selections will circulate downstream from there to create a safe software improvement lifecycle. So, given that even safe growth practices can still be bypassed, which security controls should you adopt? There are further measures that might be taken to bolster your cell banking app’s protection together with.

    We differentiate two versions of the same app if they’ve the identical bundle name and different SHA256 hashes. The oldest one among the many two versions is decided considering the dates of addition to AndroZoo. Therefore, the date of addition to AndroZoo is representative of the age of the app in the retailer. On the one hand, 13 over 59 MBAs are African child banking apps.As illustrated in Table 4, all of them inherit safety issues from African parent banking apps, representing a mean of 37% safety points inherited.Moreover, at least 17% of their safety issues are new ones. A random initialization vector (IV) ensures that encrypting the same information a quantity of times leads to different ciphertexts.

    The Means Ahead For Cell And On-line Banking Security

    digital signature definition cryptography

    While handy, it additionally introduces new security considerations that would put banking data and financial info at risk. There are on-line banking vulnerabilities distinctive to cell devices and person habits. This article delves into these dangers, explores the challenges posed by mobile banking safety, and examines the measures customers and financial institutions can adopt to mitigate them.

    Understanding these dangers and adopting greatest practices might help reduce vulnerabilities and defend delicate information. Use AI to automate the work out of defending your cell banking enterprise. Rapidly deploy all or any of 400+ cellular app security, anti-fraud, anti-bot, geo compliance, anti ATO and and different defenses in Android & iOS cellular banking apps through one platform.

    • In some apps, can get these credentials and steal sensitive credentials backend credentials are hard-coded for connection to an information from the backend useful resource.
    • Safety and engineering teams can coordinate which app variations are being focused, the standing of evolving threats, and risk metadata to mitigate future danger by using insights to build protections into future app builds.
    • The OWASP Cellular Utility Security Verification Standard (OWASP MASVS) groups the relevant controls beneath MASVS-AUTH (authentication and session management), MASVS-STORAGE (credential protection), and MASVS-PLATFORM (secure inter-component communication).

    Can Pattern-matching Sast Tools Detect Mobile App Vulnerabilities That Lead To Account Takeover?

    cryptography news

    Q-mast embeds safety directly into your workflow to prevent users from being exposed to dangers posed by insecure apps. From code to produce chain, it performs complete testing to pinpoint vulnerabilities early and guarantee safe app releases from the beginning. Public Wi-Fi networks are notoriously insecure, making them a main goal for cybercriminals. When you hook up with an open community, attackers can eavesdrop on your exercise, probably capturing login credentials or other delicate information. Cellular banking actions over public Wi-Fi significantly increase your risk of publicity to cyber threats. On the opposite hand, 6 over 59 MBAs are International child banking apps.

    You need agility to guard the mobile banking enterprise, app and customers from cyberattacks, fraud, social engineering and extra. On Appdome, groups monitor attacks and choose the security measures wanted in each launch. Then, Appdome’s patented know-how codes the safety into the mobile banking app, totally automating the build, signing, functional testing and security certification within the https://www.electionsscotland.info/5-takeaways-that-i-learned-about-4/ CI/CD pipeline. Cell banks are required to protect customer assets, prevent account takeover, reduce chargeback prices, and detect and prevent fraudulent actions their cellular banking apps.

  • The Future Of Quantum-resistant Cryptography

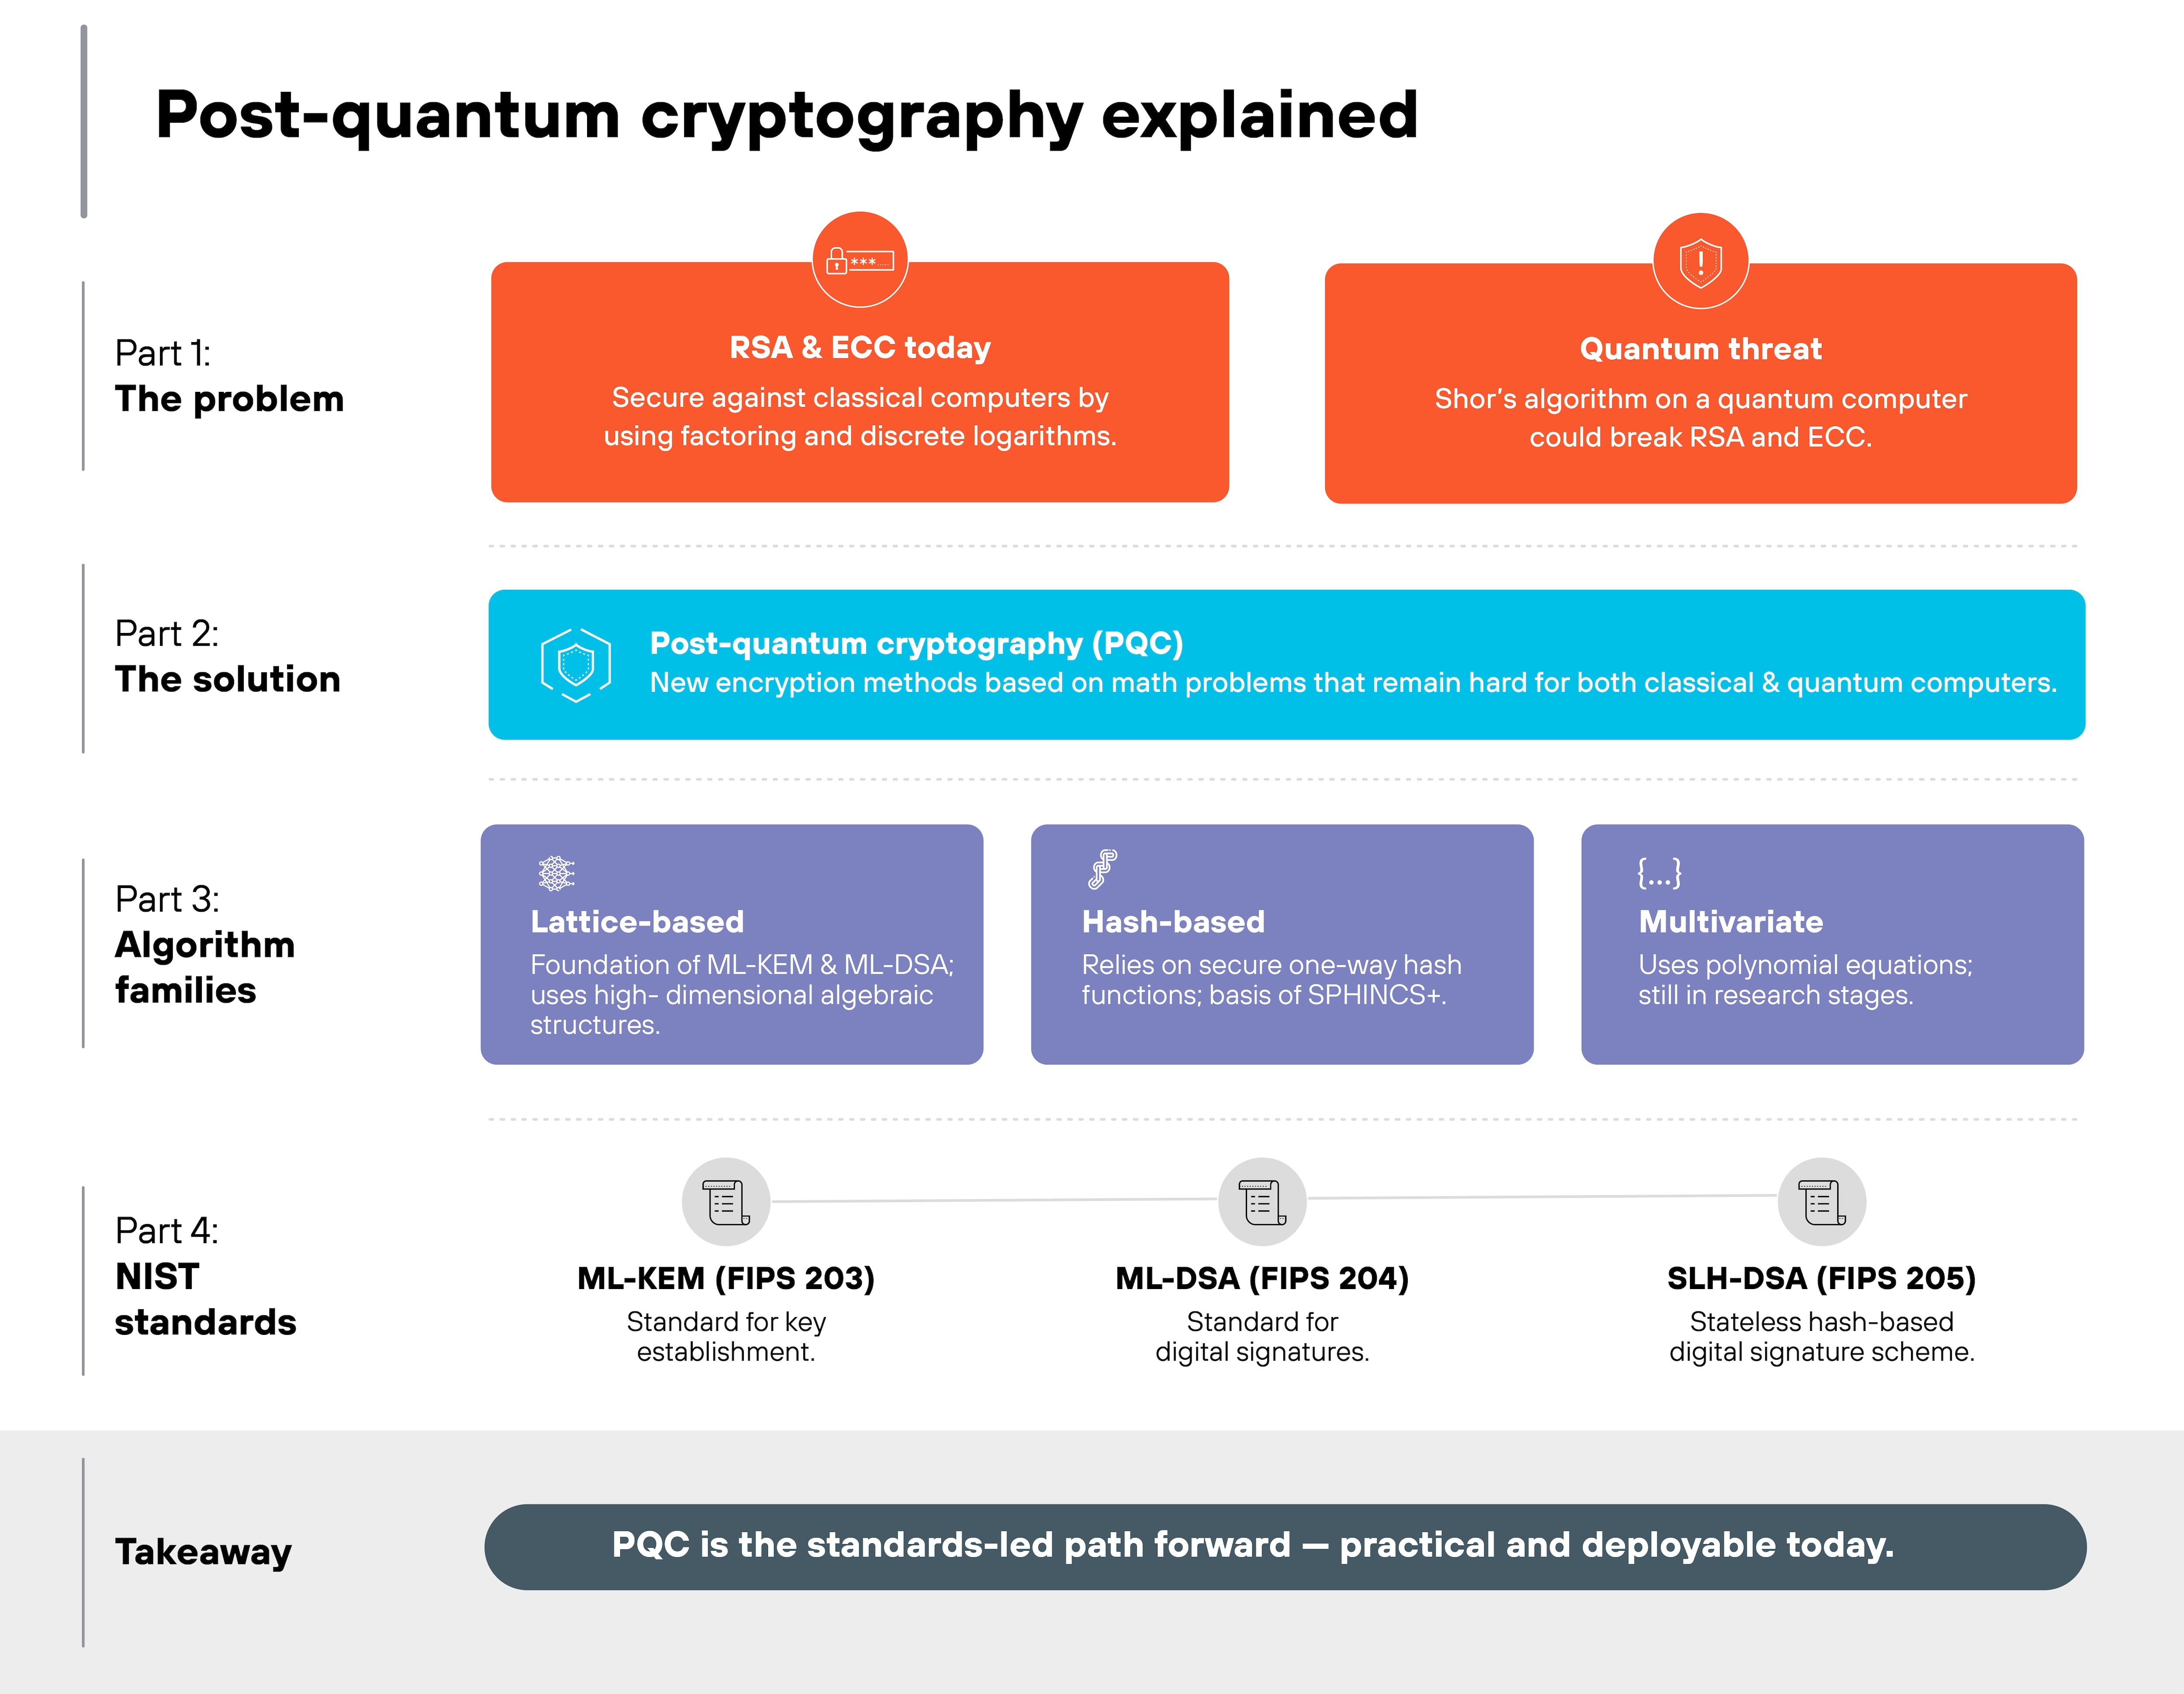
    Nevertheless, it is price noting that quantum computers are not general-purpose supercomputers. According to Ericsson Security Analysis, they are greatest understood as specialized machines able to fixing explicit mathematical problems, not a replacement for the computers we use today. Most generally used public key algorithms, like RSA and Elliptic Curve Cryptography, are vulnerable to Shor’s algorithm. They will have to be replaced with post-quantum public key algorithms currently undergoing standardization by NIST and other standardization bodies globally. To guarantee a easy transition to post-quantum cryptography (PQC), organizations can leverage Fortanix’s centralized platform to consolidate and control cryptographic operations. Fortanix Key Perception supplies organizations with a strong device to find, assess, and remediate their cryptographic environment in preparation for the post-quantum cryptography (PQC) transition.

    Shield Encryption Keys With Luna Hardware Safety Modules

    Quantum-resistant encryption, additionally called post-quantum cryptography (PQC), refers to new encryption methods designed to resist attacks from quantum computers. These strategies do not rely on the identical mathematical issues that quantum computers can easily remedy. Each check with cryptographic algorithms designed to face up to assaults by quantum computer systems. Other terms that you would be come throughout include Quantum Proof Cryptography or Quantum Resistant Cryptography. As quantum computing advances, the cryptographic algorithms defending today’s techniques will finally become susceptible. Preparing now means understanding where cryptography is applied all through your systems, figuring out long‑lived dangers, and establishing a transparent https://www.baskentmuhendislik.com/genies-updates-its-software-program-improvement-package-and-companions-with-gucci-giphy-techcrunch.html roadmap for transitioning to quantum‑safe safety.

    What About Data In Transit Versus Data At Rest?

    Anybody can use the receiver’s public key to scramble knowledge, which solely the receiver can unscramble utilizing the personal key. This method can be used to transfer symmetric keys and might even be utilized in reverse for digital signatures—because private keys are unique to the receiver, receivers can use them to validate their identification. When quantum computer systems become highly effective sufficient, they may theoretically crack the encryption algorithms that hold us protected.

    hardware security key

    Quantum computers will ultimately turn into powerful sufficient to break public key-based cryptography, also identified as uneven cryptography. Public key-based cryptography is used to protect every little thing https://www.baskentmuhendislik.com/the-newbies-information-to-web-optimization.html from your online communications to your financial transactions. Built on field-upgradable FPGAs, Thales High Speed Encryptors (HSEs) ship crypto-agility for the PQC transition. They support ML-KEM (FIPS 203), ML-DSA (FIPS 204), and SLH-DSA (FIPS 205), alongside sovereign algorithms. Hybrid, in-field upgradable configurations strengthen key change and authentication whereas sustaining compatibility with existing infrastructure as requirements and requirements evolve.

    white box cryptography

    Why Are Quantum Computers A Security Threat?

    This platform provides complete visibility into key usage, including human and machine identities, while constructing a comprehensive stock of sensitive information to strengthen security methods. The variety of belongings any organization handles is gigantic, necessitating triage of implementation and a tiered approach to protection. The classifications made at the stock stage will guide software of cryptographic protections proportionally to each asset’s sensitivity and risk of exposure.

    As the PQC rollout will get on the greatest way, replace your cryptographic policies to reflect new hybrid issuance guidelines, algorithm deprecation timelines, and exception dealing with processes. At this stage, certificate automation is not only a nice-to-have for an enterprise but a essential actuality that ensures the correct renewal, rotation, and revocation of certificates at scale. It turns into even more important given the numerous enhance in complexity that hybrid deployments introduce. For this reason, keep away from utilizing hard-coded cryptographic tokens or keys, which can make downstream modifications challenging and significantly extra pricey.

    Two pillars of such an approach include adapting current infrastructure for crypto-agility and introducing hybrid certificates which might be positioned by information criticality. Getting Ready for the modifications to come back will assist ensure a clean transition from legacy cryptographic algorithms to the post-quantum cryptography of the future. New digital signatures and key encapsulation mechanisms (KEMs) are needed to protect data and hardware from quantum attacks. Many initiatives have been launched throughout the world to develop and deploy new cryptographic algorithms that may substitute RSA and ECC while being highly resistant to each traditional and quantum attacks.

    • NIST has finalized the first PQC requirements, and its transition guidance is meant to help trade and authorities move away from quantum-vulnerable cryptography.
    • CRYSTALS-Kyber was chosen as a Key Encapsulation Mechanism (KEM) and CRYSTALS-Dilithium, FALCON, and SPHINCS+ have been chosen as digital signature algorithms.
    • A standard computer stores information as tiny switches that are either on (1) or off (0).
    • It becomes even more very important given the significant increase in complexity that hybrid deployments introduce.
    • It would take a modern pc trillions of years to break only one set of encryption keys using brute force.

    Public-key algorithms use a set of two keys, one that is privately saved by the recipient and one that’s made public. Transport Independent Mode (TIM) eliminates the need for public key exchange by enabling symmetric keys to be independently derived using out of band authenticated policy and accredited key derivation strategies. This prevents publicity of key materials in transit, mitigates Harvest Now, Decrypt Later (HNDL) threats and supports long-term quantum resilience. Organizations want to start out PQC migration now as a outcome of the transition is already underway. NIST has finalized the primary PQC standards, and its transition steering is intended to assist trade and government move away from quantum-vulnerable cryptography. NSA’s CNSA 2.zero steerage additionally offers organizations a clear sign to plan, budget, and prepare now somewhat than wait.

    However, there aren’t any ensures that a brand new sort of clever quantum assault, or maybe even typical assault, won’t sometime be discovered that can break these new algorithms. In this way, they slowly weed out candidates which are successfully attacked or shown to have weaknesses of their algorithm. The work of vetting candidates for the new standard falls principally to mathematicians and cryptographers from universities and research establishments. They submit proposals for post-quantum cryptographic schemes and search for methods to assault them, sharing their findings by publishing papers and constructing on every other’s different strategies of attack.

    public cryptography

    HC3’s Quantum Cryptography and the Well Being Sector document offers a helpful reminder of simply how broad the healthcare encryption footprint is. Delicate data at relaxation could reside in EHR and EMR techniques, mobile and medical devices, cloud environments, email techniques, servers, databases, backup methods, and vendor platforms. Information in transit spans telehealth and distant affected person monitoring, telemedicine, hybrid workforces, cloud entry, and medical professional collaboration tools.

  • What’s Cryptography? University Of Phoenix

    Public key cryptography (PKC), or uneven cryptography, makes use of mathematical features to create codes which may be exceptionally tough to crack. It allows folks to communicate securely over a non-secure communications channel without the necessity for a secret key. For instance, proxy re-encryption allows a proxy entity to re-encrypt knowledge from one public key to another without requiring access to the plaintext or personal keys. When people scan a bank card on an e-commerce website or log in to e mail profiles, cryptographic technologies sometimes prevent malicious actors from breaking into their accounts. The privacy and security cryptography presents additionally change the concept of cash due to developments within the cryptocurrency house. Bitcoin confirmed the world it is potential to use uneven encryption to create a secure and decentralized peer-to-peer (P2P) digital cost system.

    Understanding The Digital Trust Framework: A Information For Organizations

    • To encrypt and decrypt cryptographic info, senders and receivers need to know tips on how to “unlock” their message’s which means.
    • Figuring Out the forms of cryptography is one factor; deploying them securely with sound key administration is one other.
    • These consisted of complicated pictograms, the full that means of which was solely recognized to an elite few.

    Keys are critical in all cryptographic systems, however protocols use this software to encrypt and decrypt data in two different ways. Shifting keys between systems should only happen when the secret is encrypted or wrapped underneath an asymmetric or symmetric pre-shared transport key. If this isn’t possible, then the important thing must be break up into a quantity of components that are kept separate, re-entered into the goal system, then destroyed.

    Cryptology, which encompasses each cryptography and cryptanalysis, is deeply rooted in pc science and advanced arithmetic. The historical past of cryptography dates again to ancient occasions when Julius Caesar created the Caesar cipher to obscure the content of his messages from the messengers who carried them within the first century B.C.. Right Now, organizations like the Nationwide Institute of Standards and Expertise (NIST) continue to develop cryptographic requirements for knowledge safety. The most typical strategies embrace a secret key, a public key and hash features. Individuals and organisations use cryptography on a daily basis to guard their privateness and keep their conversations and knowledge confidential.

    Dig Deeper On Data Security & Privateness

    Luckily, British pc scientist Alan Turing created a sophisticated unscrambling machine known as the “Bombe,” helping the Allies learn how to https://www.ellecritique.com/HollowBodyElectricGuitar/full-hollow-body-electric-guitars get into cryptography technologies just like the Enigma. This will protect the organisation’s keys, improve effectivity, and guarantee compliance with knowledge and privacy laws. A widespread definition of cryptography is the apply of coding data to make sure only the particular person for whom a message was written can learn and course of the information. This cyber security follow, also referred to as cryptology, combines numerous disciplines like pc science, engineering, and arithmetic to create advanced codes that disguise the true that means of a message.

    Frequent Uses For Cryptography

    cryptography cyber security

    Even if the general public key’s recognized by everybody the meant receiver can only decode it because he holds his personal key. They require plenty of sources and turn into sluggish as they’re applied to larger amounts of information. Symmetric key cryptography makes use of a shared single key for both encryption and decryption. In symmetric cryptography, each the sender and receiver of an encrypted message will have entry to the identical secret key. In this manner, the sender and receiver of an encrypted message have asymmetrical keys, and the system is asymmetrical.

    cryptography vs encryption

    Cryptography ensures confidentiality by encrypting despatched messages utilizing an algorithm with a key only recognized to the sender and recipient. A widespread example of that is the messaging app WhatsApp, which encrypts conversations between people to make sure they can’t be hacked or intercepted. Digital signatures and hash features are used for authentication and ensuring knowledge integrity. A digital signature created with cryptography provides a method of non-repudiation, making certain that a message’s sender can not deny the authenticity of their signature on a document.

    Key trade is the strategy used to share cryptographic keys between a sender and their recipient. Cryptography is the method of hiding or coding information so that solely the individual the message was intended for can learn it. The art of cryptography has been used to encode messages for hundreds of years and continues to be used in financial institution playing cards, pc passwords, and e-commerce. At its core, the follow of encoding and decoding messages is used to stop unauthorized entry. This concept has existed for 1000’s of years, and its evolution has been shaped by human ingenuity and the altering landscape of technology. Ciphers are methods used to rework readable information (plaintext) into unreadable knowledge (ciphertext) in order that only licensed parties can understand the original content material.

    The power of a cryptographic system is dependent upon the standard of its algorithms and the randomness and secrecy of its keys, which is what makes the necessary thing onerous to guess and the system hard to interrupt. In current occasions, cryptography has was a battleground of a few of the world’s best mathematicians and computer scientists. The capability to securely retailer and transfer delicate data has proved a important factor in success in warfare and business. Recording key management processes manually on paper or spreadsheets runs the danger of human error and makes the keys highly vulnerable to attack or theft. Resilience is important for protecting the provision, confidentiality and integrity of keys. Any key that suffers a fault with no backup ends in the data the important thing protects being lost or inaccessible.

    Quantum cryptography makes use of the principles of quantum mechanics to safe information in a means that is resistant to lots of the vulnerabilities of conventional cryptosystems. Unlike different forms of encryption that rely on mathematic principles, quantum cryptography is based on physics to safe knowledge in a way that’s theoretically resistant to hackers. As A Result Of it is unimaginable for a quantum state to be noticed without it being changed, any makes an attempt to covertly entry quantum encoded data would be immediately recognized.

  • What Is A Cryptographic Inventory?

    Scanners miss cryptography embedded in closed merchandise and appliances, and each technique sees solely its personal layer. The CISA, NSA and NIST factsheet recommends asking vendors for lists of embedded cryptography to shut that gap. If cryptographic inventory were easy, each organization would have accomplished it by now. In actuality, several factors make this course of exceedingly tough and time-consuming. Confirm that cryptographic discovery mechanisms are employed to identify all cases of cryptography within the system, together with encryption, hashing, and signing operations.

    Scanners

    This dynamic nature means the stock process should account for changes (usually by incorporating continuous monitoring, as we’ll discuss). Microsoft is just one instance, saying it’s going to transition important services to post-quantum cryptography (PQC) by 2029 source. The firm stated cryptographically related quantum computer systems could arrive before expected, and that organizations should begin making ready now. As the pioneer and leader in Cryptographic Agility Administration solutions, InfoSec International secures the world’s knowledge by helping organisations uncover, stock, remediate, and control their cryptographic property with agile cryptography. From cryptographic asset discovery to ensuring a seamless transition to stronger cryptographic standards, our options restore digital trust to enterprises and governments.

    Qryptocyber Platform

    how does cryptography work

    Following Keyfactor’s 2025 acquisition of InfoSec International, the AgileSec Analytics platform is now a part of Keyfactor’s offering. AgileSec is an agent-based, host-centric tool that deploys lightweight sensors on endpoints, or leverages current brokers like Tanium or CrowdStrike, to scan methods for cryptographic artifacts. It searches file techniques, registries, and reminiscence for keys and certificates, identifies cryptographic libraries and their versions, and inspects configurations and API calls on each machine. NIST’s NCCoE has validated this know-how as a half of its PQC migration initiative. The major economic buyer is the Chief Data Security Officer or VP of Security, who owns cryptographic governance, audit posture, and quantum-readiness strategy. For MSSPs and consulting companions, the client is the service-delivery lead answerable for managing the multi-client cryptographic posture.

    aws payment cryptography

    Certificate Discovery: Discovering Every Certificate

    • This complete CBOM becomes a cornerstone of the security architecture – providing visibility into cryptographic use across the enterprise and enabling measured progress toward cryptographic agility and compliance in both IT and OT realms.
    • As part of Microsoft’s dedication, the corporate stated it’ll take away hard-coded algorithmic assumptions and construct techniques in which algorithm upgrades are routine somewhat than emergencies.
    • Start with an exterior TLS scan, then connect the Kubernetes agent and cloud KMS integrations to achieve internal property.
    • Define and apply cryptographic insurance policies that align with each inner governance and evolving regulatory frameworks, simplifying audits and compliance reporting.
    • Monitor for violations and ensure accountability across teams and environments.

    Tech leaders and governments around the world have set tangible post-quantum objectives, and enterprises are following swimsuit. The most successful will be those that first discover each key, certificate, and algorithm of their environment. Fortanix Information Safety Supervisor (DSM) handles the administration and remediation a part of the equation. DSM combines centralized key management with a FIPS Degree 3-certified HSM, keeping an accurate, audit-ready document of managed keys. It additionally integrates with external key companies and bring-your-own-key fashions so you can manage them all underneath one set of insurance policies.

    cryptography codes

    It calls for cautious strategy, a mix of automated tools and manual effort, and shut coordination across the organization over a long interval, typically years for big enterprises. Performing this stock is hard, but it units the stage for all subsequent steps. IBM’s cryptographic inventory ecosystem is constructed across the Cryptography Bill of Supplies concept that IBM contributed to the CycloneDX 1.6 specification. IBM also open-sourced a CBOM toolkit (CBOMkit) via the Linux Basis.

    Monthly for the parts that change most (CI/CD outputs, deployed companies, certificates). The discovery pipeline ought to be automated so refresh is reasonable https://falconline.net/ger/TreasureBoxFlash.php. For a small org with a single Git repo and a handful of companies, it can be carried out in a few engineer-weeks. For an enterprise with thousands of repositories and tens of hundreds of providers, it’s a multi-quarter project. The weak spot is that they typically report library identity (e.g., “uses OpenSSL 3.0.12”) without specifying which cryptographic primitives are actually invoked. Cryptography is now not one thing you verify on once a year.